Secure APK Distribution for Internal Testing – Best Practices
In modern Android development, shipping high-quality applications rapidly is essential. Yet one critical component often overlooked is secure APK distribution during internal testing. Sharing pre-release builds involves not just ease of access, but the rigorous protection of proprietary source code, intellectual property, and user privacy.
Whether you are an independent developer or managing an enterprise mobile team, safeguarding internal distribution is fundamental. In this guide, we review essential security best practices and examine how Flybuilds makes the entire workflow safe, professional, and compliant.
Protect Your Pre-Release Builds
Implement role-based permissions, expiring links, and encrypted storage with Flybuilds.
Why Secure APK Distribution Matters
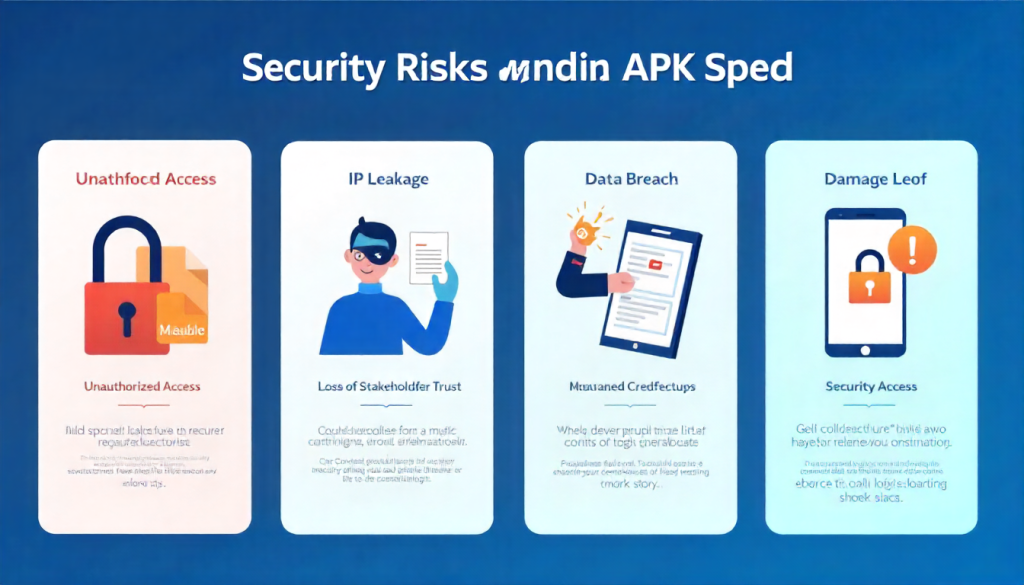
Distributing APKs exposes your pre-release intellectual property to testers, employees, and third-party collaborators. Insecure distribution channels introduce severe vulnerabilities:
- Unauthorized Access: Binaries intercepted or downloaded by unauthorized individuals.
- Intellectual Property Leakage: Unreleased features or proprietary algorithms made public prematurely.
- Data Breaches During QA: Test credentials or staging APIs exposed in unencrypted channels.
- Erosion of Stakeholder Trust: Compromised builds damaging client confidence and brand reputation.
Best Practices for Secure APK Distribution
- Use Encrypted Transfer Channels: Always enforce HTTPS/TLS protocols for uploads and downloads to prevent man-in-the-middle attacks.
- Set Download Expiration Dates: Pre-release builds should never reside online indefinitely. Enforce automatic link expiry after set durations or download thresholds.
- Track Distribution with Audit Logs: Maintain detailed logs recording who downloaded each build, the timestamp, and device metadata.
- Attach Release Notes and Test Context: Clear instructions ensure testers evaluate the proper features without risking unintended data exposure.
- Sanitize API Keys and Secrets: Never hardcode production API credentials in internal test builds.
How Flybuilds Enables Secure APK Distribution
Flybuilds was engineered specifically to address mobile build security without compromising developer velocity:
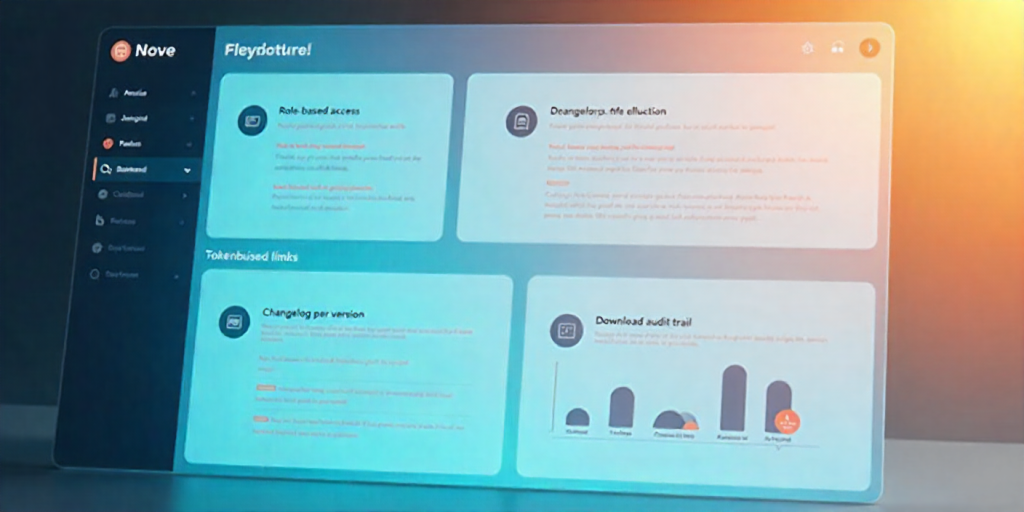
- Tokenized, Expiring Links: Share unique install links that automatically invalidate after use or time expiration.
- End-to-End Encrypted Storage: All binaries are encrypted both at rest and in transit.
- Detailed Audit Trail: Real-time logging of user downloads, IP addresses, and device profiles.
Benefits of Secure APK Distribution with Flybuilds
| Benefit | Description |
|---|---|
| Enhanced Security | Encrypted transfers, and tokenized download links. |
| Efficient Testing | Testers receive the correct build with comprehensive changelogs and instructions. |
| Compliance Ready | Complete audit trails and download records support internal security policies. |
| Professional Delivery | Branded, mobile-responsive install pages strengthen client trust. |
| Faster Feedback | Builds are delivered securely and tested faster with zero distribution friction. |
Never Compromise Security for Speed
Experience secure, professional APK distribution with Flybuilds today.
Conclusion
As mobile apps handle increasingly sensitive data, securing your internal build pipeline is essential. By implementing role-based access, tokenized links, and audit trails with Flybuilds, you can distribute builds rapidly while guaranteeing absolute security and compliance.